Scottish technology companies are moving quickly from AI experimentation to routine operational use, but the rush to exploit machine learning is colliding with a more prosaic — yet dangerous — governance problem: what to do with the phones, tablets and other endpoints organisations no longer need.
AI adoption is rising, device management hasn’t kept pace
New data from the ScotlandIS industry survey shows the scale of the change. Almost all respondents report using artificial intelligence in some form. The proportion saying AI is fully embedded in operations has doubled to 18%, while only 2% said they had no AI use at all.
Those headline figures explain why boardrooms are prioritising AI. But experts and regulators caution that increased digital workflows create a heavier dependence on employee devices for authentication, customer data and internal communications. When devices reach the end of their life, informal disposal practices can leave organisations exposed.
"AI is the headline, but device governance is still the plumbing"
Why old devices remain a corporate threat
A retired smartphone is rarely just obsolete hardware. According to the analysis, old devices can:
- still contain sensitive company data
- remain linked to corporate accounts or mobile-device-management systems
- hold authentication apps or cloud credentials
- represent a resale value that encourages informal disposal
- create an audit gap when organisations cannot account for their whereabouts
The security risk arises not from every handset leaking data, the report stresses, but from the uncertainty informal disposal creates. Organisations may not know whether a device was factory-reset, removed from management platforms such as Apple Business Manager or Android Enterprise, had its SIM or eSIM deactivated, or remained signed into corporate Google or Microsoft accounts.
Regulatory expectations and practical steps
The Information Commissioner’s Office (ICO) is explicit that organisations should use and document secure disposal methods for electronic records and hardware. The regulator expects businesses to:
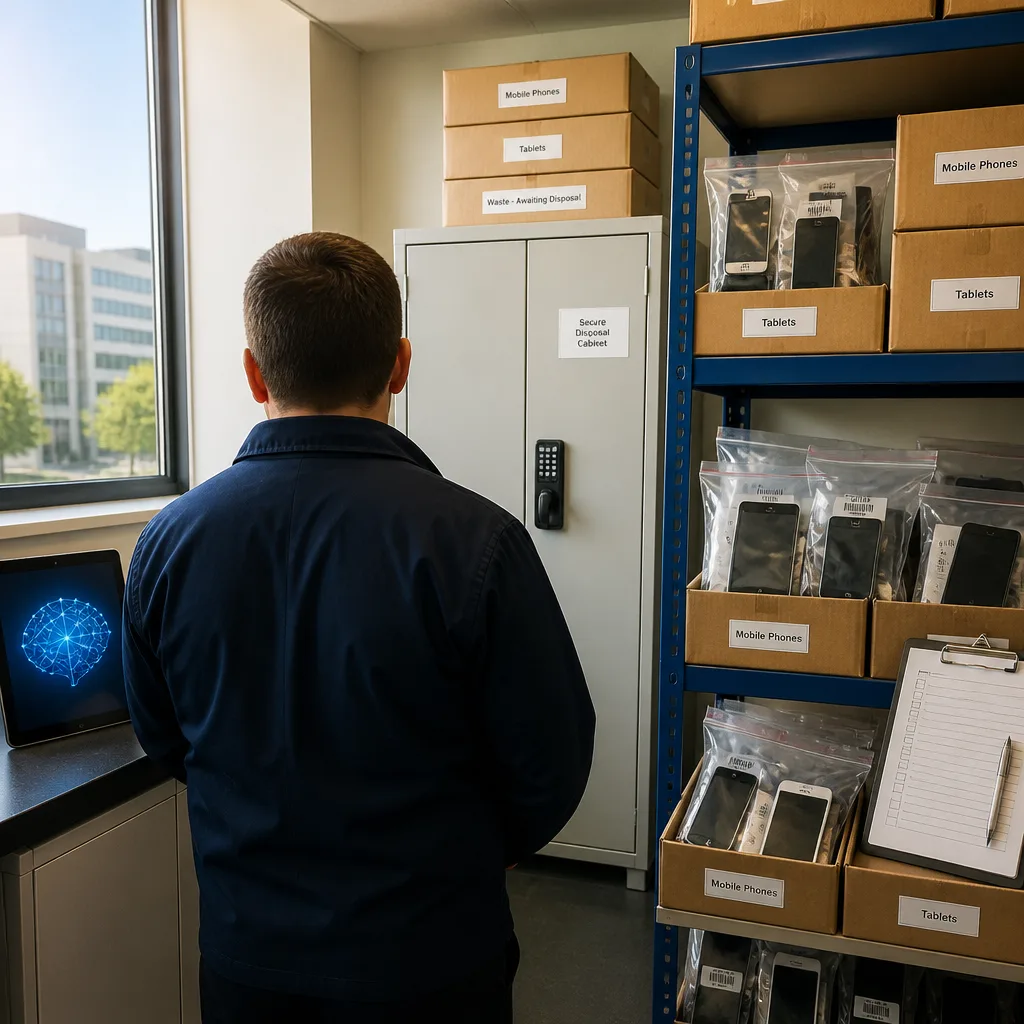
- keep devices awaiting destruction secure
- maintain logs of disposal actions
- obtain evidence of secure destruction from third parties where relevant
Those requirements matter more as AI drives more sensitive data and access tokens onto endpoints. Broader deployment plans identified in the ScotlandIS survey — spanning product development, marketing, sales, data management and cyber security — increase the number of credentials, messages and customer records that pass through employee devices.
| Measure | Survey result |
|---|---|
| Full AI adoption | 18% (doubled) |
| No AI use | 2% |
Governance, not glamour, matters
For many technology leaders the excitement of deploying generative or predictive AI is understandable. But the Scotland analysis underlines a simple reality: effective device governance is the unspectacular foundation that makes advanced digital programmes safe and auditable. Without clear records and secure disposal processes, companies risk regulatory scrutiny, data breaches and erosion of customer trust.
Practical measures — inventory control, documented sign-off for disposals, routine checks that devices are removed from management platforms and formal destruction certificates from vendors — are straightforward to adopt. The challenge will be ensuring those basics are not overlooked in the push to monetise AI initiatives.
As Scottish firms scale AI from pilots into everyday workflows, executives should treat end-of-life device handling not as an afterthought but as part of any responsible digital rollout. The plumbing of device governance matters because it protects the very systems AI depends on.